Essentials for OT
Guidance to help organisations and cyber security practitioners protect operational technology environments from sophisticated cyber threats.
At a glance
This chapter provides organisations and cyber security practitioners guidance on how to apply the ASD Essentials framework to operational technology environments. The guidance outlines eight domains, grouped into priority phases to support organisations to progress through implementation.
Key actions
Understand the ASD Essentials framework structure and how it applies to OT environments.
Familiarise yourself with the Domains and risk context and how these apply to your organisation.
Understand the priority phases to inform implementation planning for your organisation.
Introduction
The Australian Signals Directorate (ASD) provides cyber security advice and services to government, critical infrastructure, industry, small business and individuals. Part of that function is publishing prioritised, practical guidance that helps organisations direct their finite resources to the mitigations that matter most. This Essentials series chapter is designed to help these organisations protect operational technology (OT) environments from cyber threats.
What is operational technology
OT systems are those that detect or cause a direct change to the physical environment through the monitoring or control of devices, processes and events. OT includes the simple automation systems found in everyday environments as well as large and complex systems controlling critical infrastructure (CI). While the principles addressed in this chapter are applicable to all OT, the target audience of this chapter of the Essentials series includes operators of OT responsible for complex systems control, automation and safety across critical service sectors.
Critical service sectors include public transit systems, critical supply chain logistics, power generation, transmission and distribution, water and wastewater, medical services provision and large-scale industry. Securing and maintaining OT is crucial for minimising disruption to critical services.
The term vital OT is used in this document to reference the subset of critical systems that it is unacceptable to have offline for an extended period, from the perspective of the safe provision of a minimum viable product. This definition takes into consideration the ability to maintain critical operation through manual processes and implementation of Business Continuity Plans (BCP).
ASD Essentials framework structure
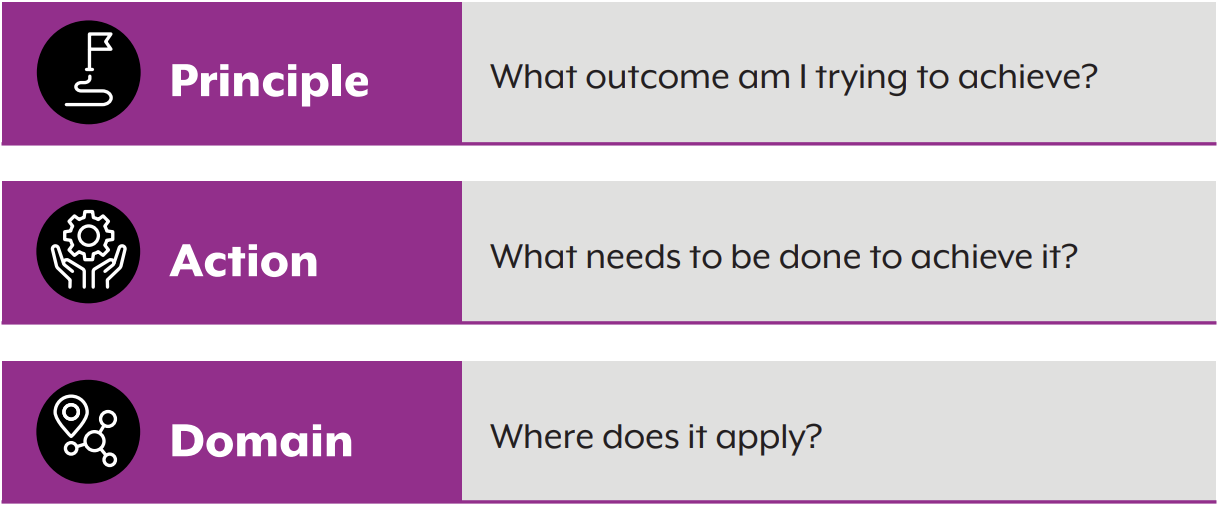
Every ASD Essentials chapter uses the same three layers:
- Principles describe the security outcomes an organisation aims to achieve.
- Actions describe what must be done to achieve them.
- Domains describe where that work applies.
The three layers answer a sequence of implementation questions, as shown in Figure 1.
To implement an Essentials series chapter, an organisation works through each action in the domains to which the action applies. The remaining content supports this implementation.
More about the Essentials
The ASD Essentials series includes the following suite of publications and guidance:
Overview publications
- Reading guide
- What is the Essentials series
- The case for change
- The Essentials for senior executives
- Which chapter should I start with?
ASD Essentials series chapters
Supplemental publications
- Transitioning from the Essential Eight
- Implementation planning guide
- Assessment process guide
- Future publications
Small and medium sized businesses that do not operate at the scale of critical infrastructure can still use this chapter where relevant. For example, the security outcomes described by the principles within the Essential series are equally important for smaller organisations. What differs is how those outcomes are achieved and how much responsibility sits with service providers and vendors.
ASD publishes tailored cyber security guidance for small businesses, home offices and individuals.
OT chapter elements
Domains
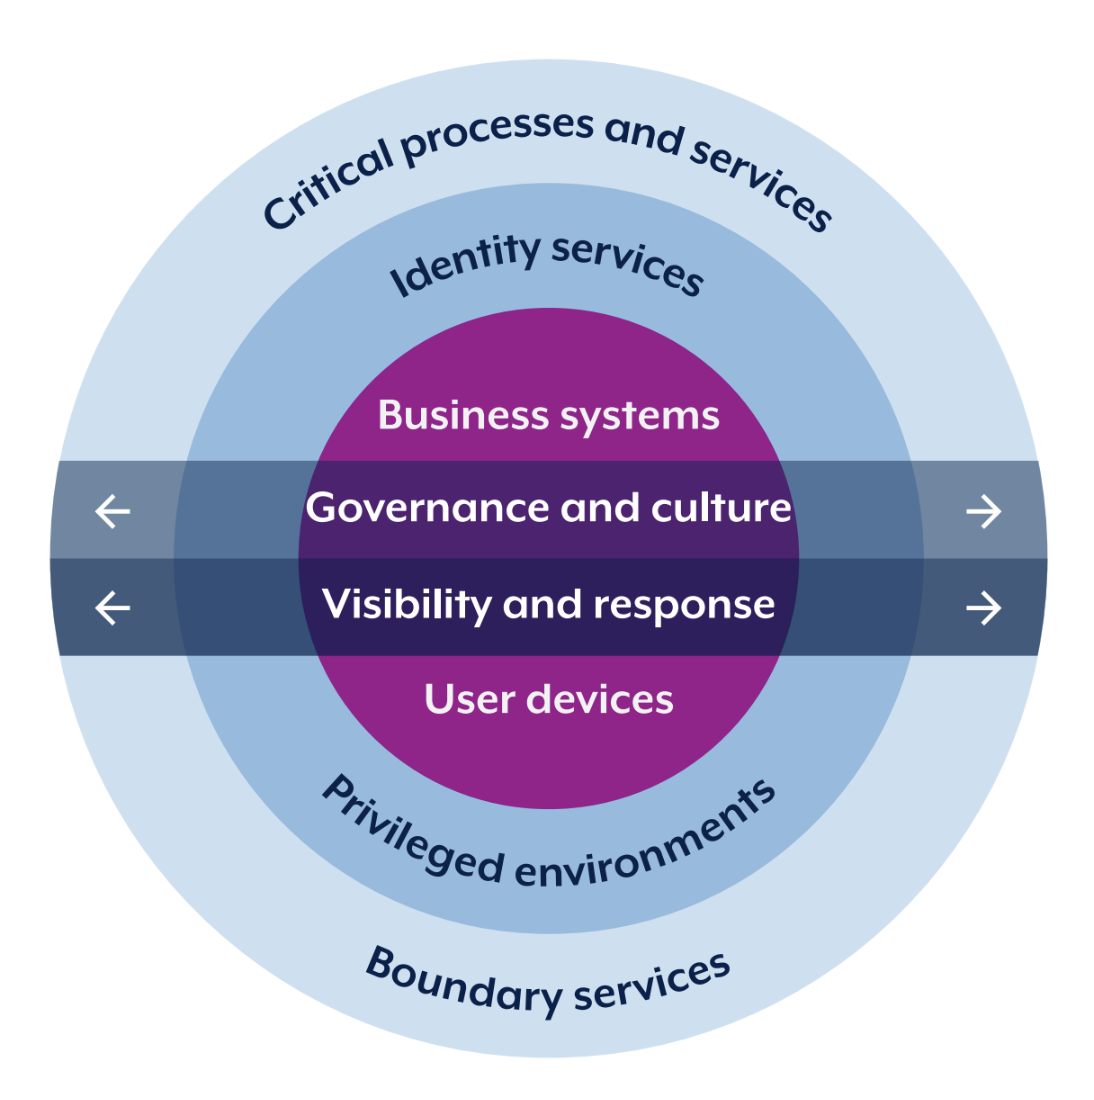
The chapter defines eight domains. Six technical domains group systems, services and assets that share similar cyber security risks.
Non-production environments, including development, testing and staging, are in scope. Assign them to domains on the same basis as any other asset, according to their function, connectivity, data, privileges and potential impact on production.
Some non-production environments can reach production or change what runs in it. Where an environment holds production trust, administrative access, or the ability to modify or deploy to production, organisations should protect it to the same level as the production environment it can affect.
Two capability domains – Governance and culture, and Visibility and response – apply across all technical domains. Table 1 describes each domain and the cyber security risk it addresses.
The description of the User devices domain in the Essentials for OT chapter is written to highlight that the risk associated with introducing endpoint-type devices to any OT environment is extremely high. Subsequently, all devices within the OT system must be considered as privileged and treated accordingly. The User devices domain is therefore not considered within the technical domains mapping later in the chapter.
The Essentials for OT chapter is to be read with application of the definitions in the ASD Essentials glossary.
| Domain | Description | Risk Context |
|---|---|---|
| Governance and culture | Policies, risk management processes, roles and security culture that underpin cyber security program. | Unclear ownership and accountability can lead to inconsistent security decisions and outcomes degrading over time. |
| Visibility and response | Procedures and capabilities for detecting, analysing and responding to cyber security events and incidents. In OT, visibility often has a second use in engineering fault analysis. | Limited visibility and response can delay the detection, analysis and containment of intrusions. In OT, this could lead to potentially catastrophic system failure. |
| Critical processes and services | Core systems and networks which are essential to safely deliver the product or service for which an organisation exists. | Compromise or loss of these systems can disrupt the organisation’s ability to deliver critical outcomes or services. |
| Boundary services | Assets at network boundaries that broker connectivity between environments of different trust levels, including internet-facing services, edge devices and points of connection to other OT systems. | Internet-facing and boundary services may be routinely exposed to adversary scanning and exploitation making them common targets for initial access. |
| Identity services | Identity, credential and access management services such as directories, authentication and authorisation services or credential stores. | Compromise of identity services can enable an adversary to gain persistent or privileged access across the enterprise. |
| Privileged environments | Systems, services and devices that support privileged activities, management services and high-impact administrative functions. Within OT, this includes items which, in an enterprise IT context, would be considered user or endpoint devices. | Compromise of privileged systems can give an adversary extensive control over systems, services and security controls. Within OT, any device with connectivity within a privileged environment must be considered a privileged device. |
| Business systems | Supporting enterprise functions that collectively enable organisational operations. | Compromise can disrupt day-to-day operations and provide pathways to more sensitive or critical systems. Business systems may exist within the IT systems of an organisation, with their OT process support possibly making them considered part of the OT systems. |
| User devices | Endpoints issued to the workforce, including desktops and laptops. | The critical nature of OT systems, coupled with the high-risk cyber security possibilities present in many environments, should prohibit the use of typically configured end-user or endpoint devices within OT environments. Use of such devices risks the unintended introduction of cyber threats directly into the privileged OT environment. All devices within the OT system must be considered as privileged and treated accordingly. |
Priority phases
In each chapter, the domains are grouped into priority phases. The phases set out the order in which ASD recommends the domains be addressed. This reflects where ASD assesses that effort delivers the greatest and most rapid reduction in risk.
Priority phases are a sequencing mechanism, not a rating. They do not represent assurance over the effectiveness of controls, compliance against a standard or an organisation’s cyber security maturity against a particular class of adversary. The recommended sequence is designed to support organisations to progress through each phase, scaling and hardening their environments as they go, reducing the organisations’ overall cyber security risk.
The technical domains are sequenced differently in this chapter to reflect the operational safety requirements of OT environments. OT cyber security prioritises the safe and continuous operation of physical processes. This can require greater emphasis on protecting critical processes, controlling connectivity and administrative access, and using compensating controls where changes such as patching or replacing legacy equipment cannot be made without affecting operations.
The technical domains are grouped into the following priority phases:
Priority phase 1: Boundary services and Critical processes and services
Boundary services are prioritised because they provide pathways between OT systems and external or less trusted environments. Critical processes and services are prioritised because their compromise or disruption could have significant safety, operational, environmental or service-delivery consequences. Addressing these domains together strengthens the protection of pathways into the OT environment while protecting the systems and processes with the greatest potential consequence.
Priority phase 2: Privileged environments and Identity services
Privileged environments and Identity services control administrative and privileged access to OT systems. Weaknesses in these domains can allow an adversary to gain elevated access, move through the environment or make unauthorised changes to critical systems and processes. Addressing these domains together reduces the likelihood that an initial compromise can escalate.
Priority phase 3: Business systems
Business systems are addressed after the domains that protect critical operations, connectivity and privileged access. This sequencing reduces the likelihood that compromise of a business system can provide a pathway to critical OT systems while strengthening the protection of business functions that support OT operations.
The two capability domains (Governance and culture, and Visibility and response) apply across all phases and expand as implementation progresses.
ASD recommends implementing the technical domains in the sequence shown to focus cyber security effort where it provides the greatest benefit against current adversary tradecraft.
Refer to the Implementation planning guide for detailed planning advice.
ASD Essentials for OT matrix
Matrix structure and use
Each principle states a cyber security objective drawn from ASD’s Information Security Manual (ISM). Principles align with the corresponding ISM principle identifier, such as GOV-01. These identifiers are provided for traceability and do not indicate an implementation order.
Actions describe what organisations must do to achieve each principle in technology-agnostic terms. Organisations implement these actions through controls that are appropriate to their IT environment, risk profile and regulatory obligations. Relevant controls can be found in the ISM and other ASD guidance.
For guidance on applying these principles and actions to artificial intelligence (AI), refer to AI considerations within the ASD Essentials series.
Where applicable, the technical domain matrix maps actions to the MITRE ATT&CK techniques they are intended to address.
The matrices are organised by capability and technical domains:
- Matrix 1 and 2 cover the two capability domains.
- Matrix 3 maps actions across the five included technical domains.
Capability domains
Governance and culture
| Principle | Action |
|---|---|
| GOV-01 - Executive cyber security accountability | Formally define and establish executive and board-level accountabilities for OT cyber security, including setting, monitoring and adjusting organisational risk appetite, and review these accountabilities at a defined cadence. |
| GOV-08 - Executive artificial intelligence accountability | Establish and maintain executive accountability for the use, governance and risk management of artificial intelligence within the organisation. |
| GOV-04 - Cyber security resourcing | Assign sufficient cyber security personnel and resources with the required skills to operate, monitor, maintain and manage the lifecycle of controls across OT, and define cyber security responsibilities within role descriptions. |
| GOV-10 - System exposure minimisation | Protect OT system information, and the systems outside the OT environment that are critical to OT functionality, as high-value assets, and prevent public disclosure of OT device installation details, requiring third parties to do the same. |
| GOV-11 - Supplier cyber security assurance | Establish and maintain a process to assess and manage supply chain risk for hardware, software and third party service providers, and to confirm that providers of services essential to OT understand the criticality of vital OT and can meet agreed levels of prioritised support. |
| Establish and maintain a process to only use software, hardware and services from trustworthy suppliers that have demonstrated a commitment to the security of, and transparency for, their products and services | |
| GOV-14 - Legacy system management | Establish and maintain a process for identifying, assessing and managing the cyber security risk associated with legacy and unsupported systems that remain operationally critical, until they can be removed or replaced. |
| GOV-07 - Continuous cyber security improvement | Conduct regular exercises of isolation and sustained isolated operation, covering isolation decision-making, threat hunting before reconnection, safe removal of isolation, sustained operation for the defined isolation period, artefact capture, and staff movement in a degraded communications environment. |
| PRO-20 - Remote access to operational technology | Notify local operators of authorised remote maintenance or supplier activity, so that unexpected changes are not normalised or ignored. |
| PRO-14 - Cyber security awareness training | Ensure all personnel receive cyber security awareness training that is tailored to how they will interact with OT systems in their assigned roles, and update it on a regular basis to reflect current threats and operational considerations. |
Visibility and response
| Principle | Action |
|---|---|
| IDE-01 - Asset identification | Use an approved asset inventory mechanism that supports automated discovery to detect new and changed assets, recording physical and logical location, role, criticality, dependencies, known vulnerabilities and existing compensating controls. |
| IDE-02 - Business criticality rating identification | Identify and document vital OT, and the enabling systems and services on which vital OT depends, including those located outside the OT environment. |
| IDE-04 - Security risk identification | Identify and analyse the OT attack surface, security boundaries and connectivity, including the points through which complete isolation can be enacted, and review these inputs on a continuous basis. |
| RES-01 - Cyber security incident planning | Update business and operational continuity plans to reflect the impact that isolation will have on business and operational processes. |
| Use documented, tested and approved OT incident response procedures when responding to cyber security incidents, covering situations such as safety events, setting out who participates in response and recovery, including third parties, loss of visibility, and workstation compromise. | |
| Establish and maintain a document management capability for system documentation, and retain per-site copies of playbooks, drawings, installation, reset and configuration instructions, break-glass secrets and keys, and emergency contact information in a form that does not depend on the systems being recovered. | |
| RES-05 - Cyber security incident coordination | Maintain alternative communications for site-to-site and site-to-staff use during degradation or loss of normal communications, and establish processes to have the right staff at the right site when isolation is enacted. |
| Build into response plans the capability to collect forensic artefacts for later offline analysis within pre-approved areas. | |
| RES-03 - Cyber security incident response | Establish, maintain and exercise a plan to rapidly disconnect remote access when malicious activity is identified. |
| RES-02 - Cyber security incident reporting | Establish and maintain an effective process, independent of systems outside the OT environment, for personnel to raise an OT cyber security concern. |
| REC-02 - System recovery assurance | Maintain the capability to recover, without supplier support, any system that cannot acceptably remain offline, at least to a minimum viable level of service, including a plan to replace key OT devices following destructive attacks. |
Technical domains
| Principle | Action | MITRE ATT&CK | Critical processes and services | Boundary services | Identity services | Privileged environments | Business systems |
|---|---|---|---|---|---|---|---|
| IDE-01 - Asset identification | Continuously identify and document infrastructure, operating systems, applications, identities, credentials and data as distinct assets. | ✔ | ✔ | ✔ | ✔ | ✔ | |
| IDE-05 - Asset interdependencies | Identify and document safety components for physical and electrical systems, including the connectivity and dependency relationships between safety systems. | ✔ | |||||
| IDE-06 - Resilience requirement identification | Identify and document the communication and alerting infrastructure that carries safety functions to external alarm systems, and assure the reliability of those paths where communication services are degraded or unavailable. | Loss of safety | ✔ | ✔ | |||
| PRO-01 - Secure system lifecycle | Design, size and configure new network devices so that network traffic capture can be enabled without a subsequent configuration change. | ✔ | ✔ | ✔ | ✔ | ||
| Sanitise and securely dispose of hardware, including devices returned to a supplier for maintenance, using trusted onsite or domestic disposal services. | Theft of operational information | ✔ | ✔ | ✔ | ✔ | ✔ | |
| PRO-16 - Cyber supply chain security | Identify, test and resolve third-party dependencies that would fail under isolation, including licensing, activation, updates, supplier support, and licences coupled to physical hardware identifiers. | Loss of availability | ✔ | ✔ | ✔ | ✔ | |
| Verify the integrity and provenance of assets, software, components and updates before they are introduced into the OT environment, and record the origin and handling history of new, repaired and serviced assets. | Supply chain compromise | ✔ | ✔ | ✔ | ✔ | ✔ | |
| PRO-13 - Identity, credential and access management | Confirm the functionality of break-glass accounts, and the availability of their secrets, for administrative access during isolation from other authentication mechanisms. | ✔ | |||||
| Use phishing-resistant MFA for users authenticating across a perimeter into OT, and from any network not under the organisation's sole OT administrative control. | ✔ | ✔ | |||||
| Ensure that credentials are unique per device or account, changing default, supplier and simple passwords before a device is commissioned or replaced, and where unique credentials are not supported, apply a compensating control that protects the device. | ✔ | ✔ | ✔ | ✔ | ✔ | ||
| PRO-12 - Least privilege access | Establish and maintain a process to grant, track and periodically review approval of all remote access users, using secure protocols and restricting access to the minimum level required for the work being performed. | Remote services | ✔ | ✔ | |||
| Provision administrative and privileged functions in OT as distinct roles, each assigned to a unique account with only the minimum access and privileges required to perform defined operational functions. | Valid accounts | ✔ | ✔ | ||||
| PRO-05 - Secure administration | Manage supporting site infrastructure from a dedicated management network within the most critical network to which it is connected. | ✔ | ✔ | ||||
| Ensure administrative, engineering and troubleshooting access to OT can only be initiated from dedicated and hardened environments that are isolated from unprivileged workloads and located in a segment of equal or greater trust than the system being administered. | ✔ | ✔ | |||||
| PRO-04 - Secure configuration management | Detect and respond to configuration changes within OT and its demilitarised zones, including changes to name resolution records, through automation or continuous technical assessment. | Modify parameter | ✔ | ||||
| Define and deploy approved configuration baselines that disable or remove unnecessary physical ports, communications ports, services, insecure settings and weak protocols where systems support it, prevent unauthorised changes to name resolution records, monitor for access attempts against exposed services, and bring critical OT elements that can be updated to the same baseline as their IT equivalents. | ✔ | ✔ | ✔ | ||||
| Harden new instances of control software, including modelling, forecasting and automated decision support systems that provide input to control, where feasible, and where doing so does not degrade the availability or safety of the OT system. | ✔ | ||||||
| PRO-06 - Vulnerability management | Apply security patches or updates within defined risk-based timeframes, record each asset that cannot or will not be patched along with the reason, and bring critical OT elements that can be updated to the same hardening baseline as equivalent critical elements in IT. | Exploitation of remote services | ✔ | ✔ | ✔ | ✔ | ✔ |
| Apply compensating protections where assets cannot or will not be patched, or where they remain operationally critical but are no longer supported by security patch release. | Exploitation of remote services | ✔ | ✔ | ✔ | ✔ | ✔ | |
| Establish and maintain a register of assets that cannot be patched, or that will not be patched, recording for each the reason, the compensating protections applied, the residual risk accepted and the authority accepting it, and review each entry at defined cadence whenever the asset's exposure changes. | ✔ | ✔ | ✔ | ✔ | ✔ | ||
| PRO-07 - Trustworthy software | Ensure only approved and integrity-verified software is permitted to execute on systems that support it, with exceptions minimised, risk-accepted, time-bound and regularly reviewed. | ✔ | ✔ | ||||
| PRO-10 - Regular and proven backups | Conduct regular testing of rebuild, backup and restoration procedures to ensure that they are reliable and capable of meeting defined recovery time objectives and recovery point objectives, including rebuilding in the absence of backups. | ✔ | ✔ | ✔ | ✔ | ||
| Backup the firmware, configuration, licence, calibration, project and logic files and supplier images required to rebuild OT, held per site and isolated from network access, on a defined schedule aligned to criticality and rate of change, and maintained to support restoration to a common point in time. | ✔ | ||||||
| PRO-18 - Network segmentation and segregation | Limit communication between OT assets and any other network to explicitly approved pathways and services, based on business requirements, location and trust levels, and design new OT systems so that each service can exist within its own network segment or enclave. | ✔ | ✔ | ✔ | |||
| Isolate OT sites and business function zones within protected network segments, with communication between them policy driven through a demilitarised zone rather than direct and unlimited. | ✔ | ||||||
| Segment safety systems from non-safety parts of the OT environment, enforced at a network boundary rather than by device configuration alone, and protect safety systems against change originating outside the site safety system boundary. | Loss of safety | ✔ | |||||
| Isolate non-production OT environments from production and from each other, where such environments exist. | ✔ | ||||||
| PRO-19 - Operational technology isolation | Establish and maintain demilitarised zones that isolate OT at its perimeters from all networks not under the organisation's sole administrative control. | ✔ | |||||
| Document the procedures used to enact isolation, including clear physical identification of the cables and equipment involved. | ✔ | ✔ | |||||
| Ensure isolation points can only be managed from within vital OT, so that enacted isolation cannot be reversed externally. | ✔ | ||||||
| Maintain the capability to isolate vital OT and sustain safe operation for a defined period aligned to critical service continuity requirements, and verify the effectiveness of isolation mechanisms on enactment and throughout the isolation period. | ✔ | ✔ | |||||
| Ensure the services on which vital OT depends operate independently of systems outside the OT environment, using separate software, credentials, storage, policy and servers, so that those services remain available throughout isolation. | ✔ | ✔ | ✔ | ✔ | |||
| PRO-20 - Remote access to operational technology | Ensure remote access is not routed directly into OT, terminating all traffic in the OT demilitarised zone before the next hop. | ✔ | |||||
| Enforce explicit session establishment controls before remote access is permitted, including time-bound grants, no permanent connections, and disconnection after a defined period of inactivity. | ✔ | ✔ | |||||
| PRO-15 - Physical access control | Maintain physical site access controls, and plan for a safe site environment for operators to work in, that continue to function in a degraded or isolated state. | ✔ | |||||
| Implement physical security controls at devices and sites where physical access poses heightened cyber security risk, and disable unused physical ports and removable media interfaces where business continuity allows. | ✔ | ||||||
| DET-01 - Centralised event logging | Perform host-based logging on operator, engineering and server systems within the OT environment, and maintain log collection, query and investigation capability that remains available when systems outside the OT environment are unavailable. | Indicator removal on host | ✔ | ✔ | ✔ | ✔ | ✔ |
| DET-04 - Baselined high-risk access activities | Record all remote access sessions with the details of the user, timestamp and target, and monitor them for deviations from validated patterns. | ✔ | |||||
| DET-02 - Cyber security event detection | Capture and monitor network traffic continuously on both sides of all OT-connected demilitarised zone boundaries. | ✔ | |||||
| Capture and monitor traffic at interfaces between segments within OT, using detection methods with a high signal-to-noise ratio, and alert on control protocols crossing segment boundaries where they are not expected. | ✔ |